No inbound port needed
The server dials out to the gateway, so it can stay unreachable from the internet.
Networks
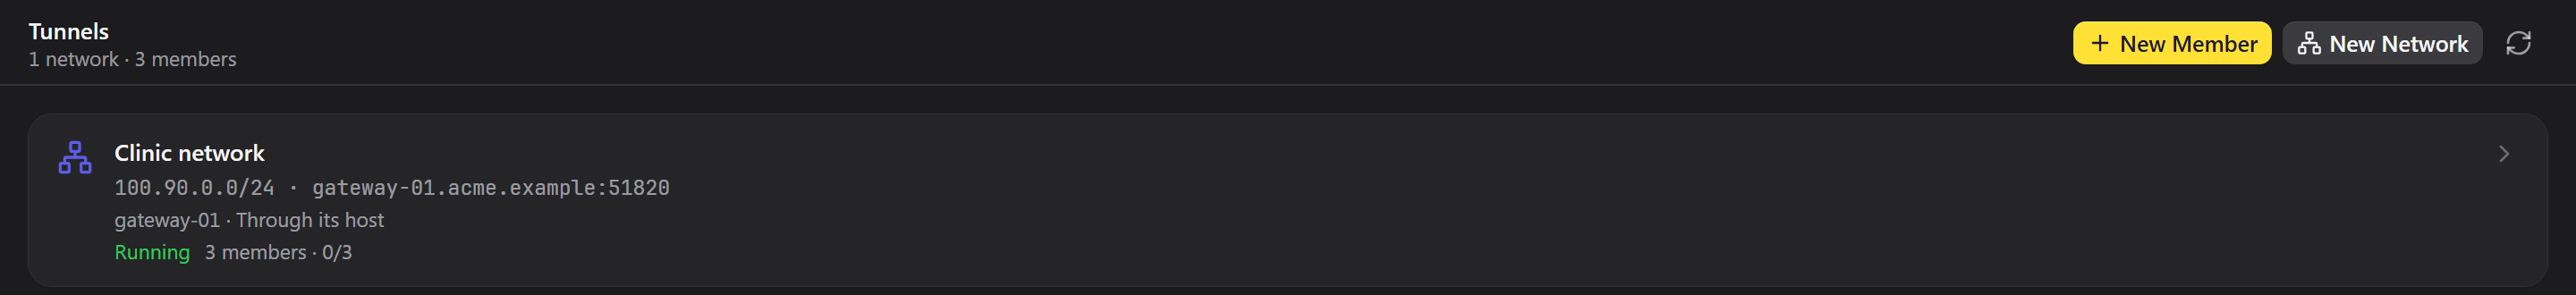
Servers behind NAT with no public address, devices on a closed clinic network, machines only your VPN can see: Zedlin has a way to each of them, and they stay closed to everyone else.
WireGuard networks
Zedlin starts a WireGuard gateway on a machine of yours over SSH. Each server joins with one line, using WireGuard from its own distribution.
How it stays closed
The server dials out to the gateway, so it can stay unreachable from the internet.
Its private key is generated there and never leaves.
WireGuard is in the kernel. No Zedlin service stays on the machine.
The tunnel interface only accepts SSH from the gateway. You decide per member whether Zedlin and other members may reach it.
Keep customers or sites apart, each with its own gateway, subnet and port.
Last handshake and traffic per member. A lost tunnel shows up as an unreachable server.
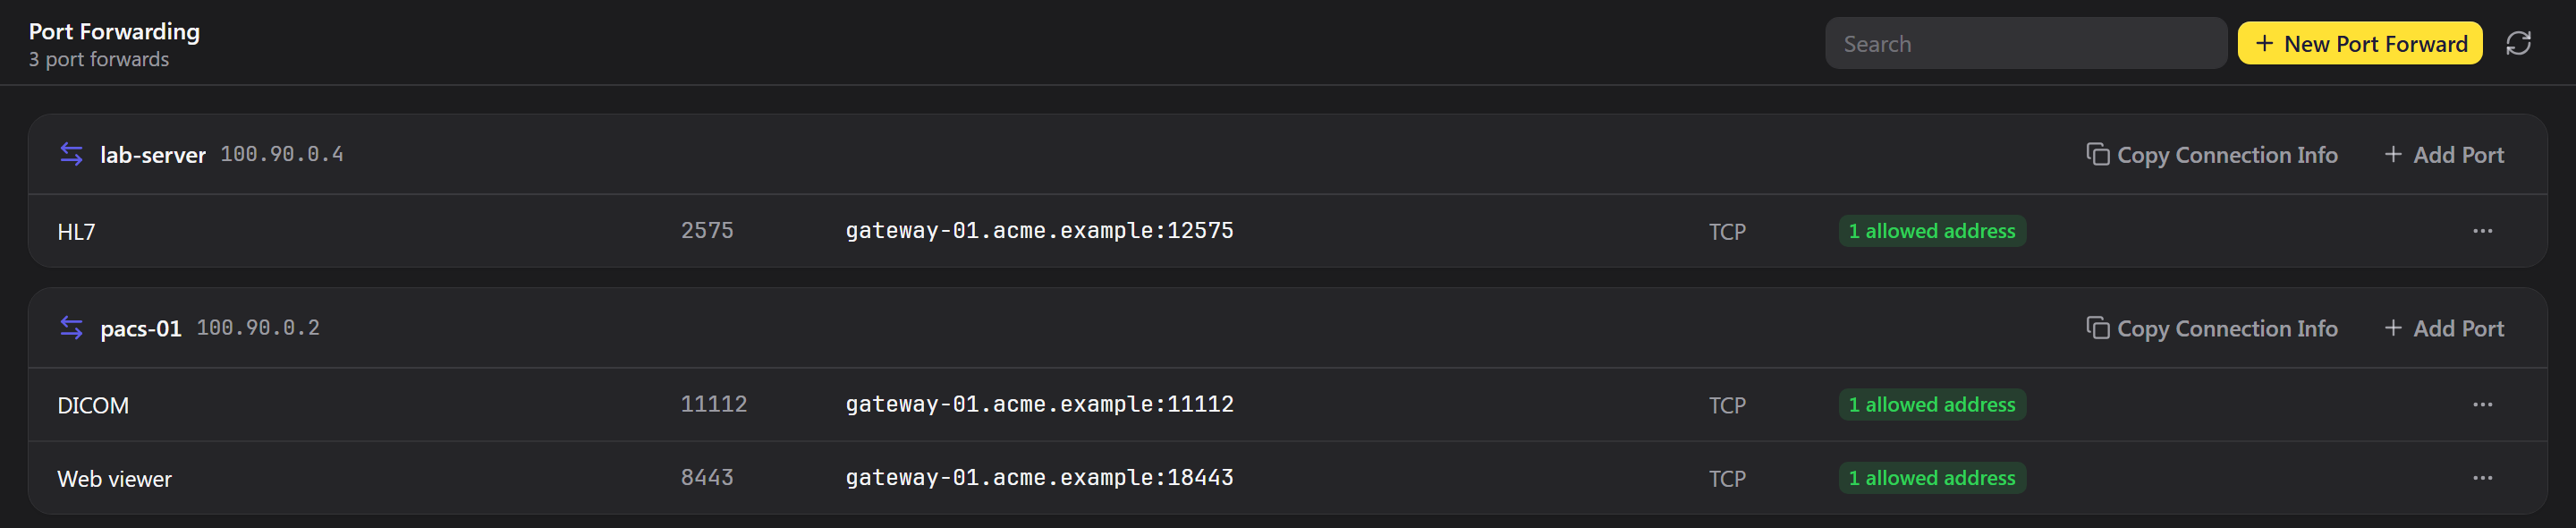
Port forwarding
Need to reach a DICOM port or a web interface on a closed network? Forward it through a Linux machine of yours, open only to the addresses you list. People connect with whatever VPN they already use.
Also in the box
Runs as an nginx container on the machine. Saving checks the config first and reloads without dropping connections.
Test the path to the target from the forwarding machine, before anyone complains.
Some servers only your laptop can reach, say over a customer's VPN. Team jobs run through the device that starts them, while the secrets stay on the server.
Limit which addresses may reach your Zedlin server. It won't let you save a list that locks you out.
Networks and port forwarding run on a Zedlin server you host yourself.