Addresses
Each IP in one row: on how many servers it is blocked, allowed or missing, and how many packets it has sent.
Firewall
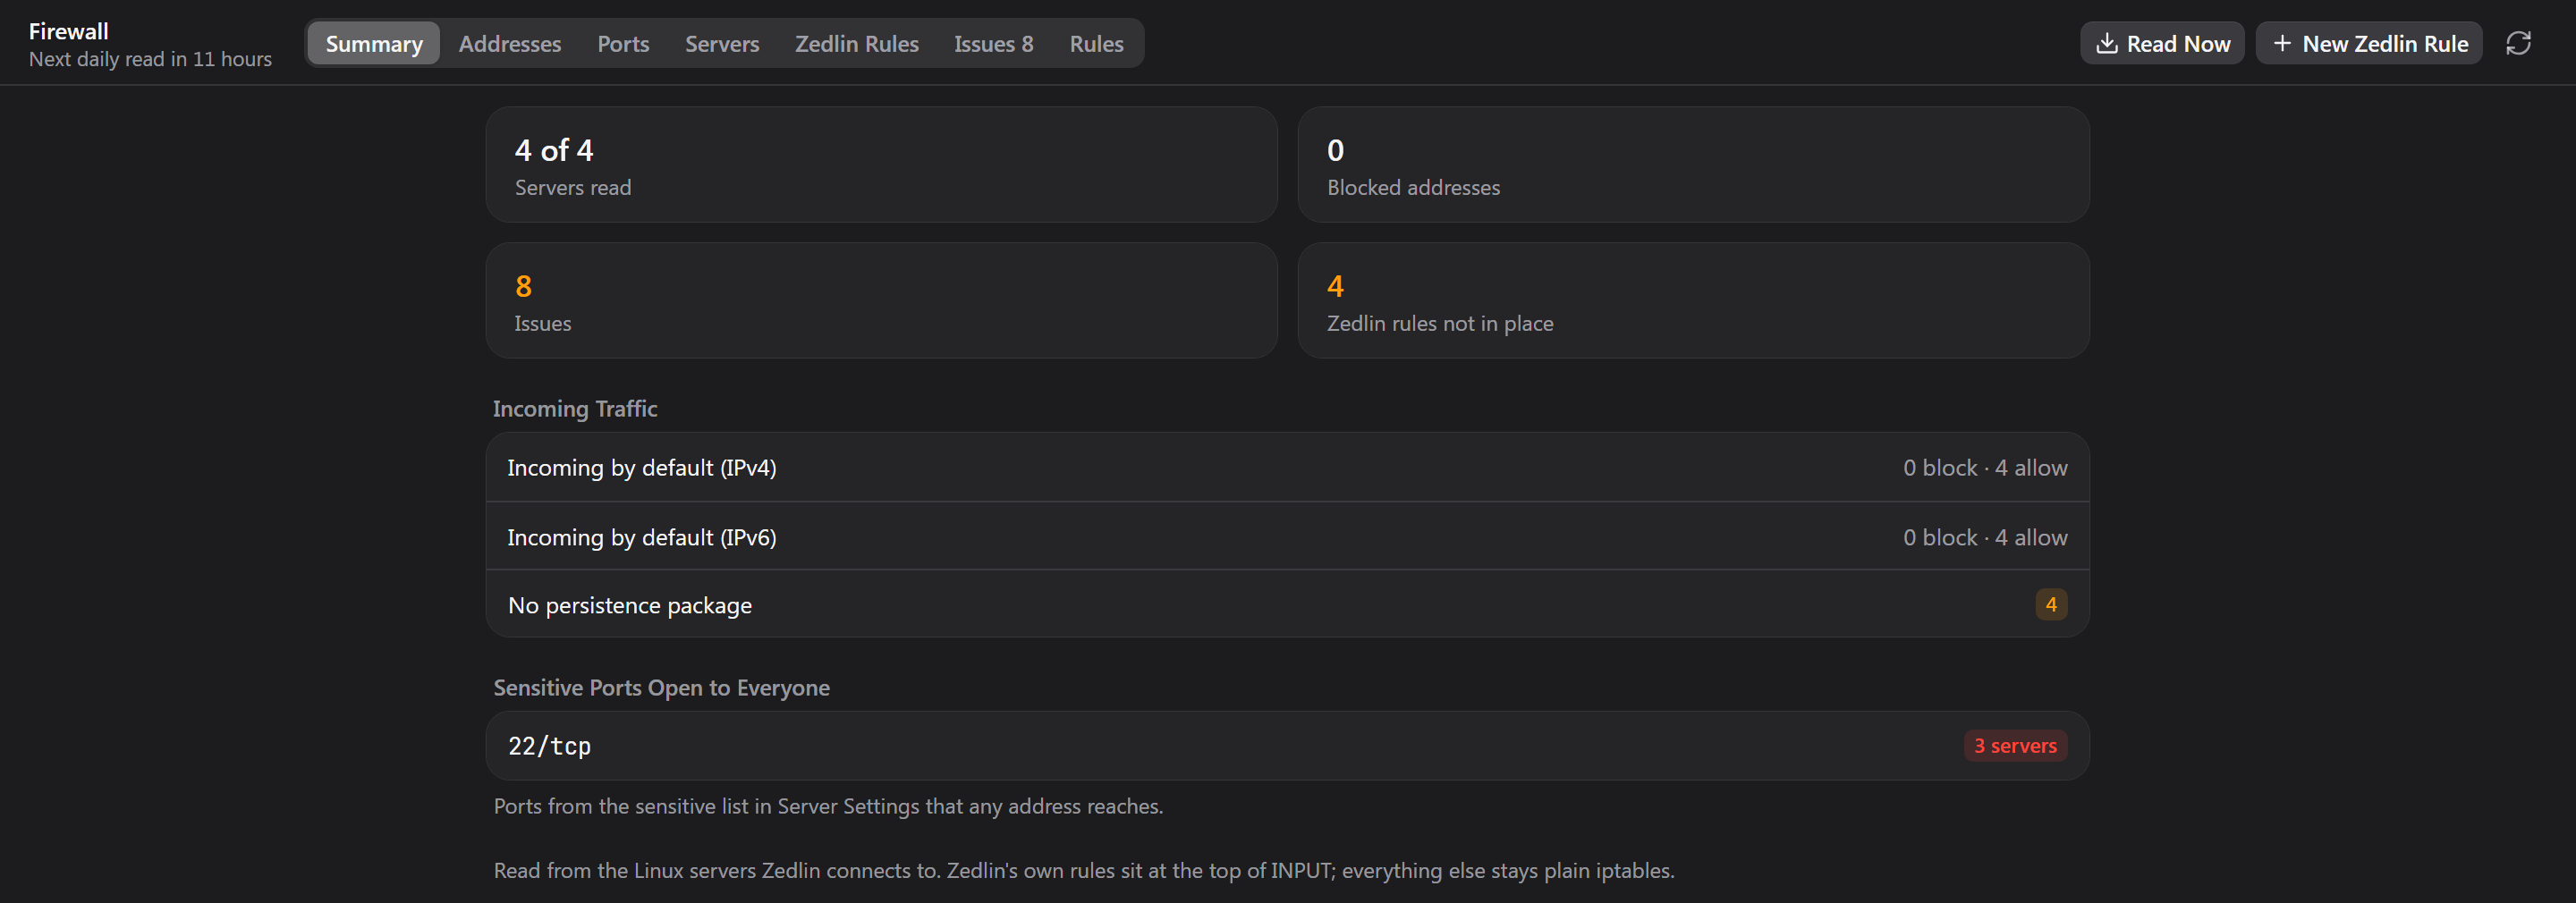
Zedlin reads iptables from all your Linux servers and answers the questions a list of rules can't: is this address blocked everywhere, which ports are open to the world, and which rules never take effect? Then you change it from one page, without fear of locking yourself out.
Analysis
Each IP in one row: on how many servers it is blocked, allowed or missing, and how many packets it has sent.
Each port: where it is open to everyone, limited or closed, what is listening, and what Docker has published.
Rules that never fire, repeats, ports closed on IPv4 but open on IPv6, and ports Docker opens past INPUT.
Default policy, rule counts, whether rules survive a reboot, and when each was last read.
Change it safely
Zedlin keeps its rules in its own chains at the top of INPUT, FORWARD and OUTPUT, and leaves your hand-written rules alone.
Apply a rule to all servers, a tag or chosen ones, and exclude a server when needed.
An hour, a day, a week or permanent, with a note saying why.
A change has to be confirmed over the same connection. If that connection dies, the server undoes it within a minute.
DOCKER-USER gets the same rules, so published ports are covered too.
A backup before every change, and a stored version whenever the rules change.
Anything unusual can still be typed as a command, with the same rollback.
Move simple INPUT and DOCKER-USER rules under Zedlin in one step, in their order.
Block an address from an alert, a threat row or the address detail.
Combine it with port scans and connection logs for the full picture.